Nitro Enclave Deployment
Coming soonRunning the cosigner inside an AWS Nitro Enclave is in testing and not yet supported for production.
Use regular mode today.
What's planned
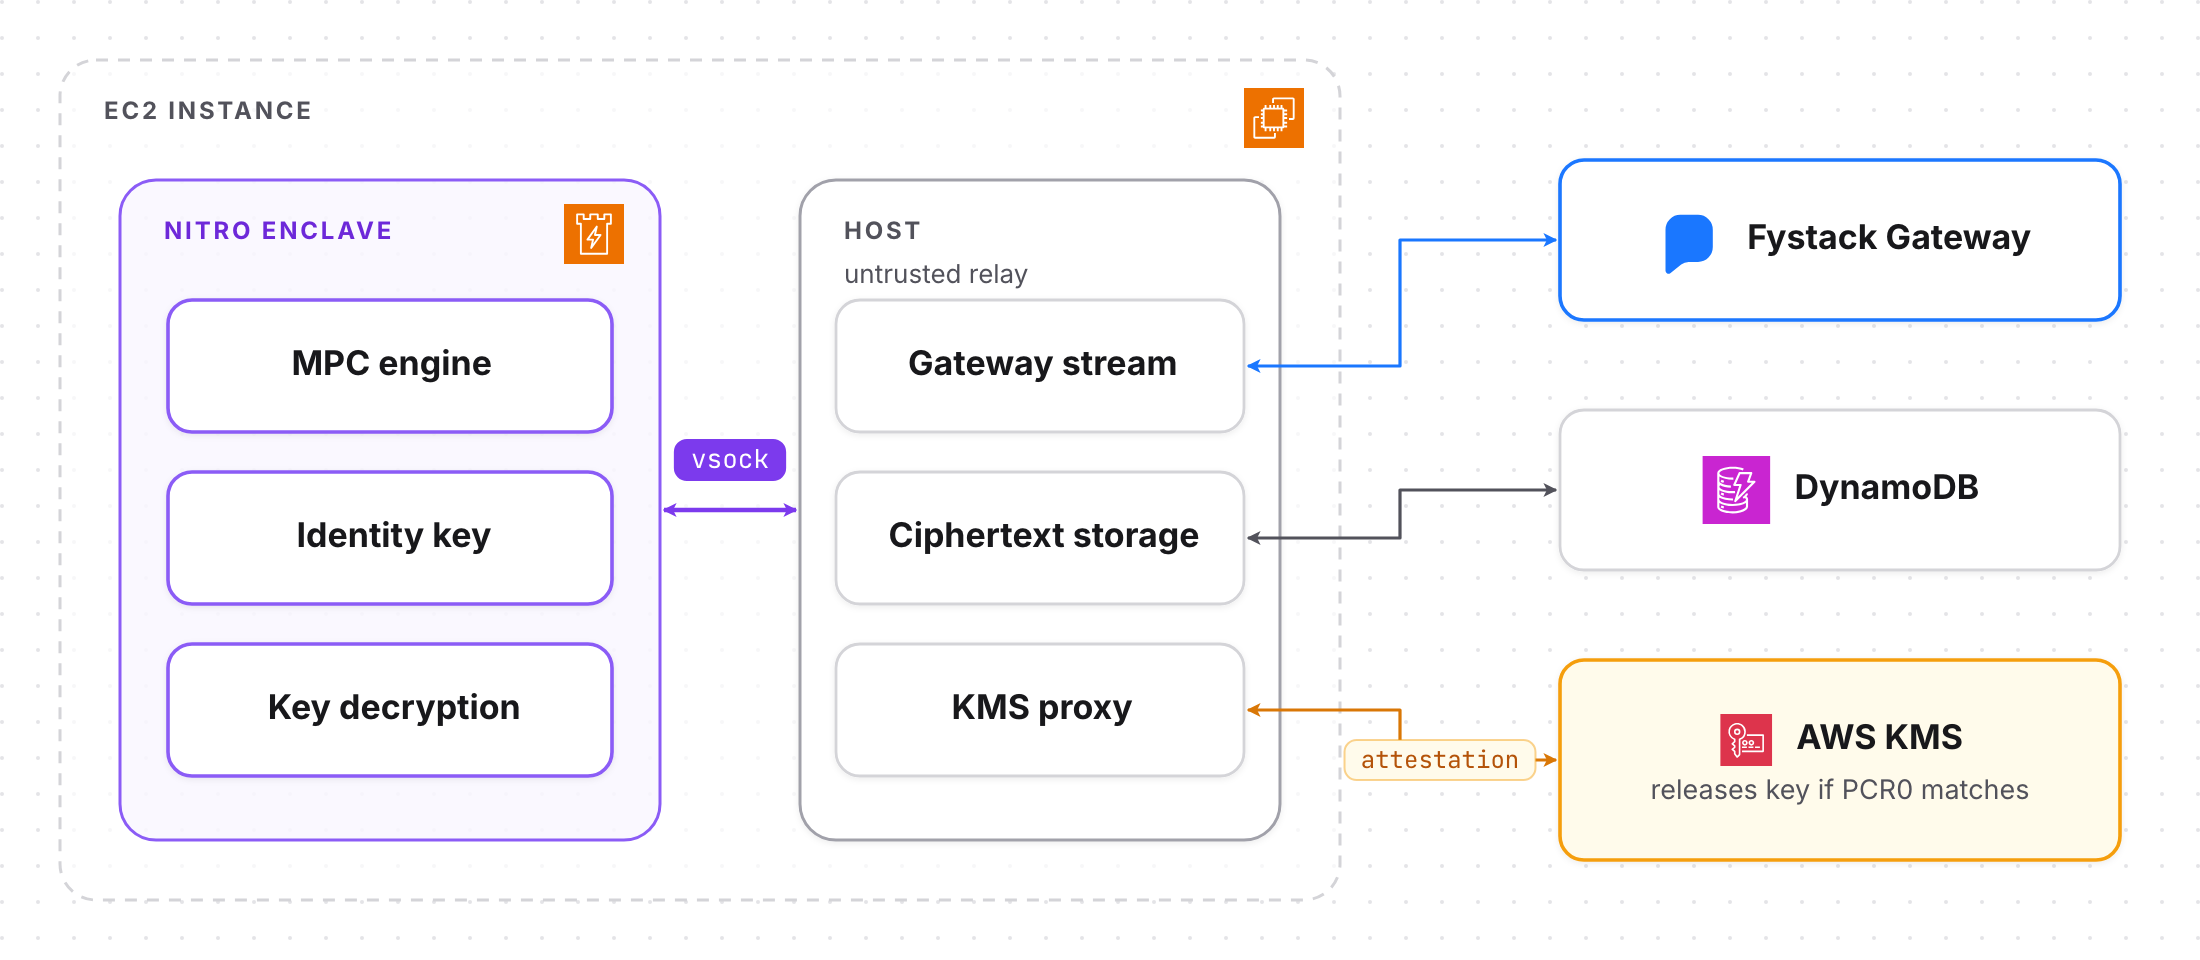
- Enclave: runs MPC, holds the identity key and decrypts key shares. No network, disk or shell.
- Host: untrusted relay for the Gateway stream, storage and KMS.
- Attested key release: AWS KMS releases the storage key only to an enclave whose PCR0 matches your key policy.
Result: host admins cannot read key shares.
Need enclave isolation now? Contact Fystack to join early testing.