Fystack Cosigner
The cosigner is an MPC participant you run on your own infrastructure. It holds one share of every wallet key and joins keygen and signing with Fystack's MPCium nodes. Before each signature it asks your approval server.
Why run a cosigner
- Shared custody: Fystack cannot reach a signing quorum without your share.
- Your policy, enforced locally: Your callback server sees the raw bytes to be signed and can reject anything.
- No inbound ports: The cosigner dials out to Fystack over gRPC with TLS.
- Signed releases: Every image and binary is Sigstore-signed.
cosigner-cliverifies and pins the digest before running. - Enclave isolation (coming soon): AWS Nitro Enclave support so host admins cannot read key shares.
Overview
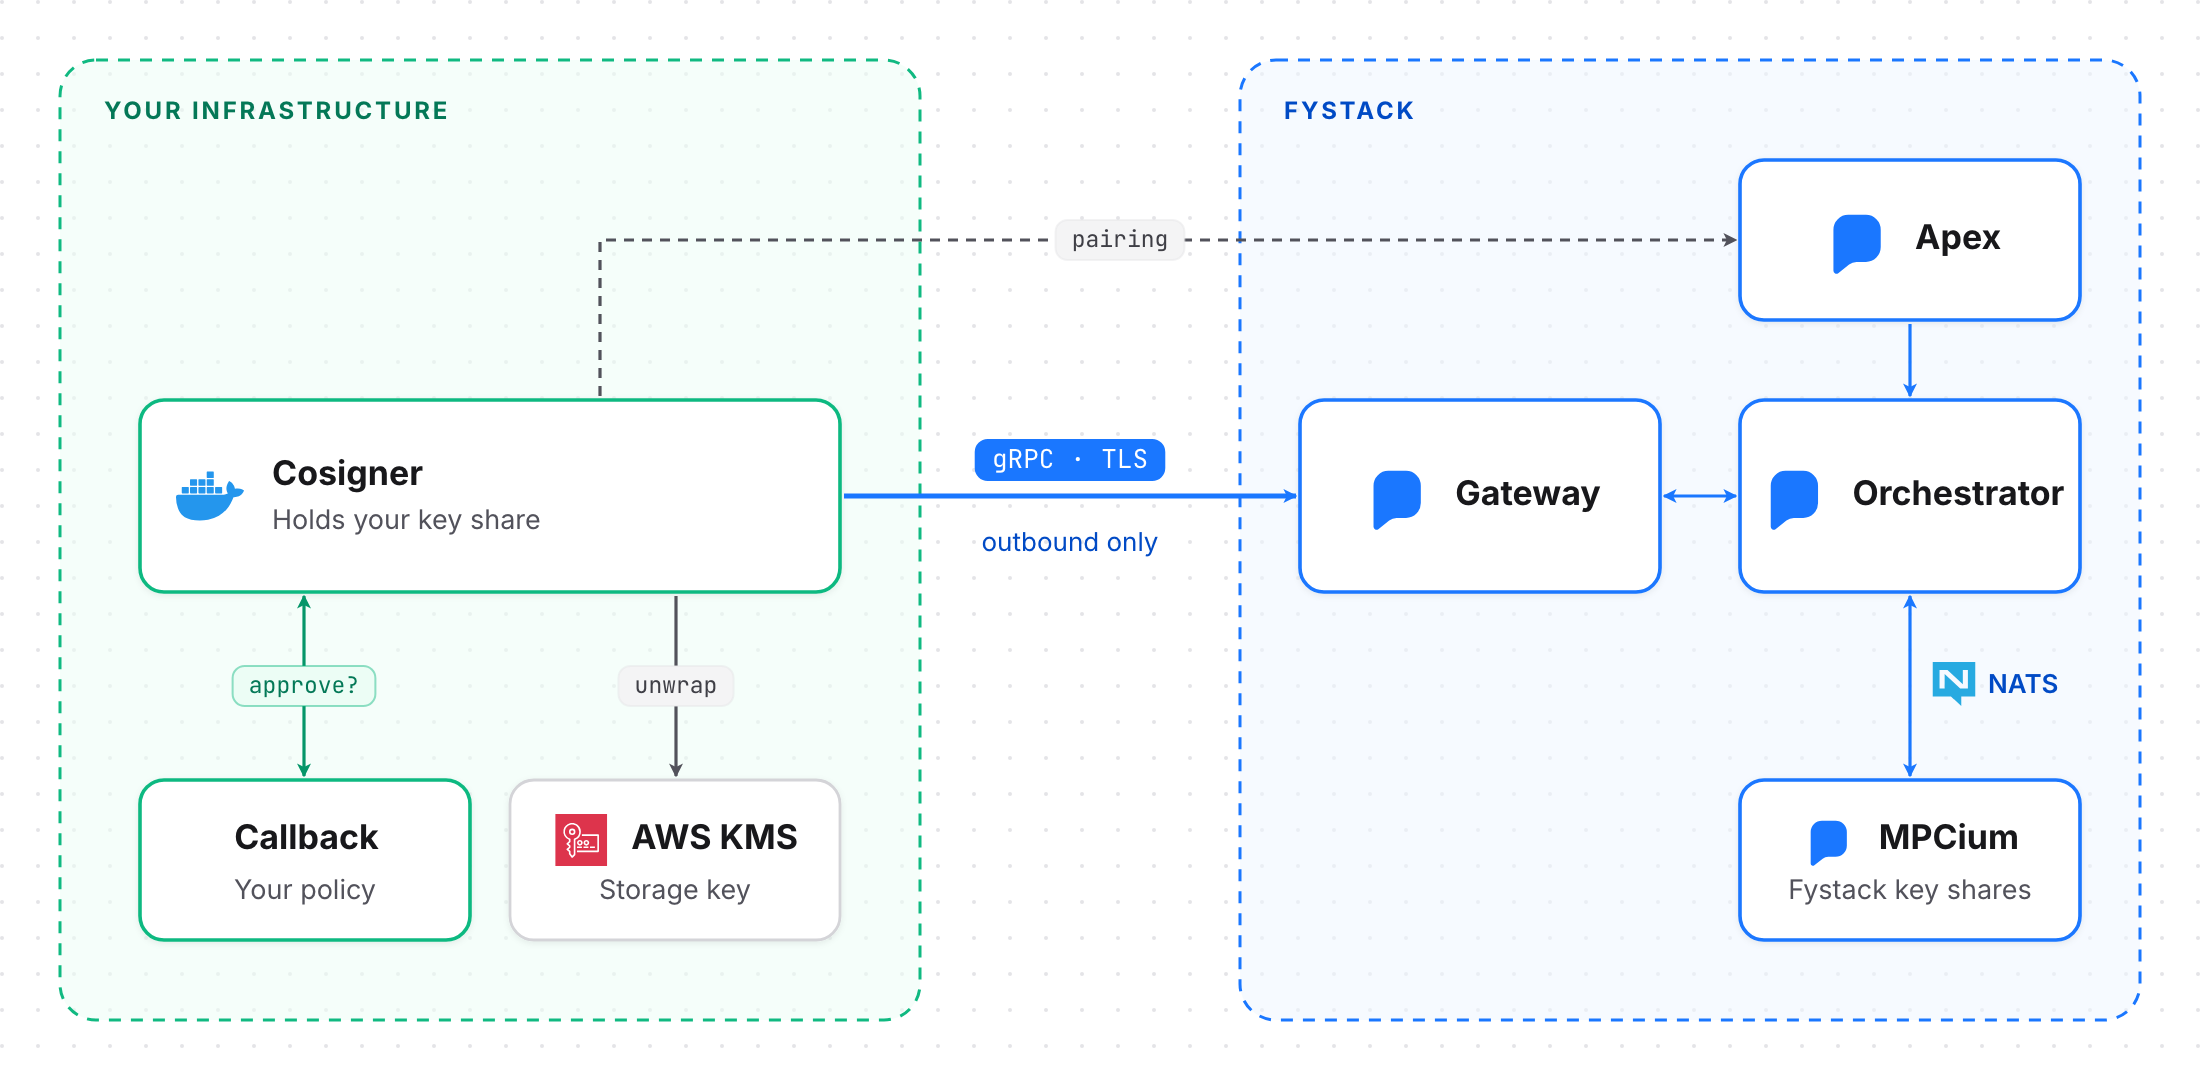
- Your side: the cosigner container, your approval callback, and a storage key source (password or AWS KMS).
- Fystack side: Apex (pairing, requests), Gateway (cosigner connections), Orchestrator (sessions) and MPCium nodes.
MPC messages are end-to-end encrypted between participants. The Gateway and Orchestrator relay them but cannot read them.
Operations
| Operation | Cosigner role |
|---|---|
| Keygen | Generates its share of ECDSA (secp256k1) and EdDSA (Ed25519) keys. No one ever holds the full key. |
| Sign | Verifies the request, asks your callback, then joins threshold signing. |
| Reshare | Rotates shares to a new committee. Public key and addresses stay the same. |
| Export | Writes encrypted .mshare files for offline recovery. |
Deployment modes
| Mode | Runs on | Who can read key shares |
|---|---|---|
| Regular | Linux + Docker, managed by cosigner-cli |
Anyone with root or Docker access on the host |
| Nitro Enclave (coming soon) | AWS EC2 with Nitro Enclaves | Only the attested enclave |
Regular mode is the supported deployment today. Nitro Enclave support is coming soon.